2020年6月27日 星期六

[CentOS-announce] Release for CentOS Linux 8 (2004)

---------- Forwarded message ---------
From: Brian Stinson <bstinson@centosproject.org>
Date: Jun 16, 2020 12:46AM

We are pleased to announce the general availability of CentOS Linux 8.
Effectively immediately, this is the current release for CentOS Linux 8
and is tagged as 2004, derived
from Red Hat Enterprise Linux 8.2 Source Code.

As always, read through the Release Notes at :
http://wiki.centos.org/Manuals/ReleaseNotes/CentOS8.2004  - these notes
contain important information about the release and details about some
of the content inside the release from the CentOS QA team. These notes
are updated constantly to include issues and incorporate feedback from
the users.

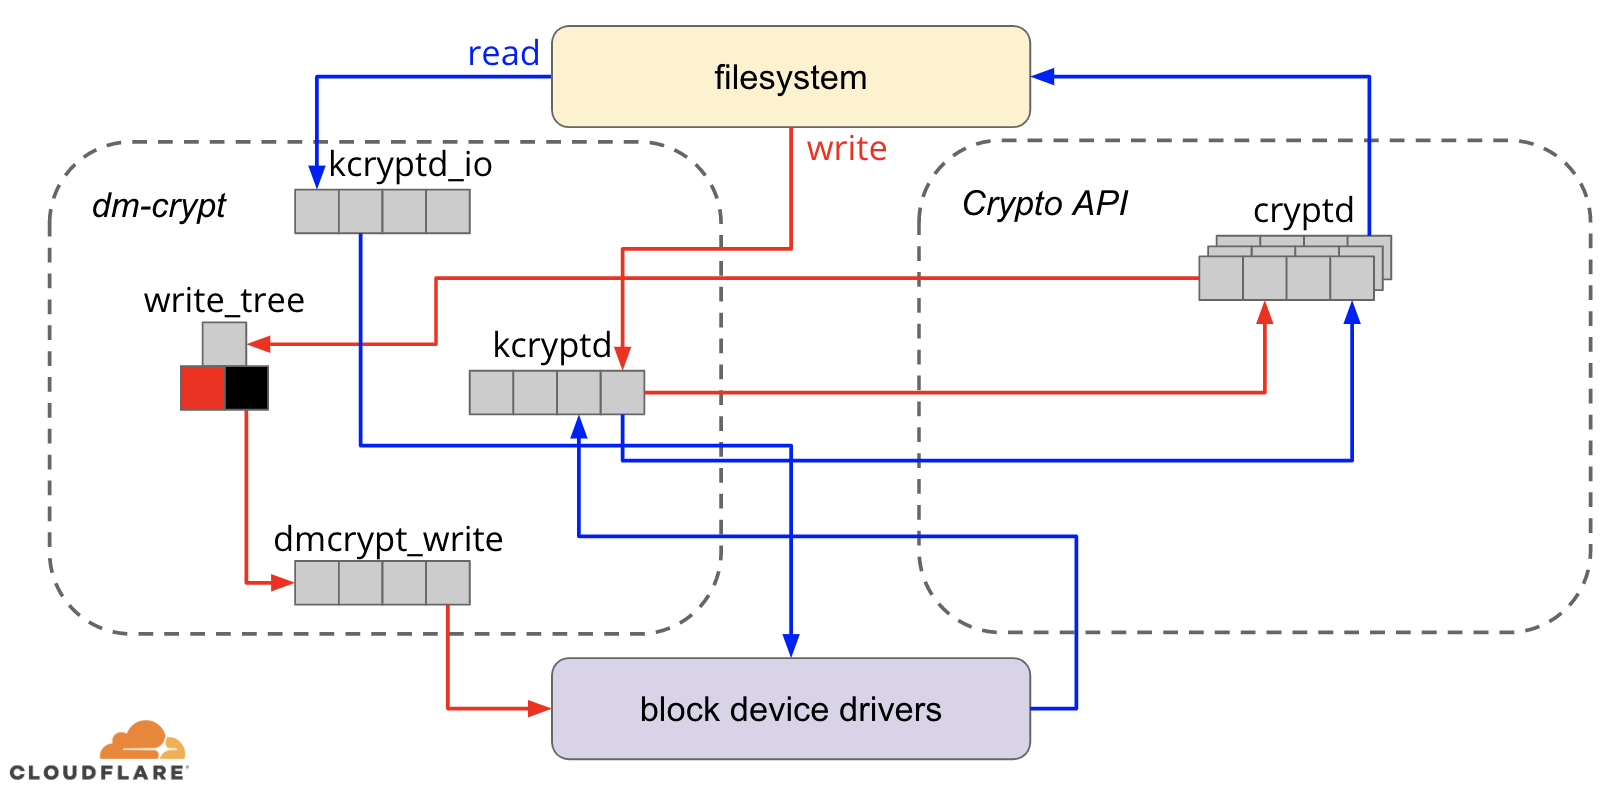
Speeding up Linux disk encryption

dm-crypt
REF: https://blog.cloudflare.com/speeding-up-linux-disk-encryption/

[openssh-unix-announce] Announce: OpenSSH 8.3 released

---------- Forwarded message ---------
From: Damien Miller <djm@openbsd.org>
Date: May 27, 2020 3:33PM

OpenSSH 8.3 has just been released. It will be available from the
mirrors listed at https://www.openssh.com/ shortly.

Changes since OpenSSH 8.2
=========================

The focus of this release is bug fixing.

Reporting Bugs:
===============

- Please read https://www.openssh.com/report.html
  Security bugs should be reported directly to openssh@openssh.com

Bitnami's First Product Launch within VMware: Tanzu Application Catalog


The Bitnami team is excited to announce our first product within VMware is part of the VMware Tanzu portfolio. Tanzu Application Catalog brings a selection of open source applications and components continuously tested and maintained for the enterprise. With Tanzu Application Catalog, developers can increase their productivity by using pre-packaged and production-ready containers and charts while operators ensure IT security and governance. Check out the announcement of TAC within the VMware Tanzu portfolio.

[USN-4367-2] Linux kernel regression

---------- Forwarded message ---------
From: Steve Beattie <steve.beattie@canonical.com>
Date: May 29, 2020 7:10AM

USN-4367-1 fixed vulnerabilities in the 5.4 Linux kernel. Unfortunately,
that update introduced a regression in overlayfs. This update corrects
the problem.

References:
  https://usn.ubuntu.com/4367-2
  https://usn.ubuntu.com/4367-1
  https://launchpad.net/bugs/1879690

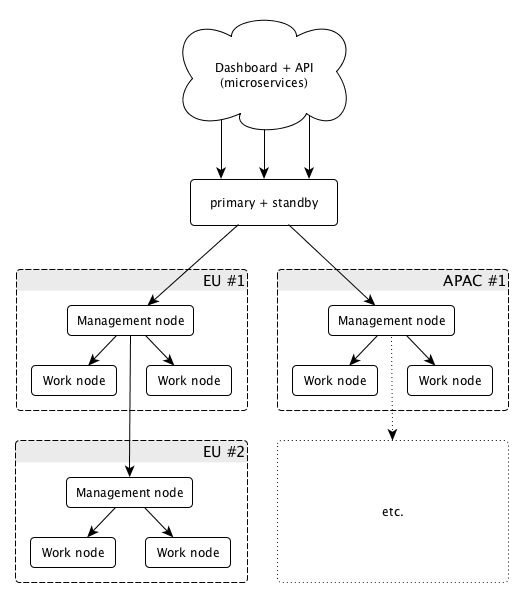
Cloudflare: Introducing Quicksilver: Configuration Distribution at Internet Scale


REF: https://blog.cloudflare.com/introducing-quicksilver-configuration-distribution-at-internet-scale/

2020年6月14日 星期日

[USN-4376-1] OpenSSL vulnerabilities

---------- Forwarded message ---------
From: Marc Deslauriers <marc.deslauriers@canonical.com>
Date: May 28, 2020 9:23PM

Cesar Pereida García, Sohaib ul Hassan, Nicola Tuveri, Iaroslav Gridin,
Alejandro Cabrera Aldaya, and Billy Brumley discovered that OpenSSL
incorrectly handled ECDSA signatures. An attacker could possibly use this
issue to perform a timing side-channel attack and recover private ECDSA
keys. (CVE-2019-1547)

Matt Caswell discovered that OpenSSL incorrectly handled the random number
generator (RNG). This may result in applications that use the fork() system
call sharing the same RNG state between the parent and the child, contrary
to expectations. This issue only affected Ubuntu 18.04 LTS and Ubuntu
19.10. (CVE-2019-1549)

Guido Vranken discovered that OpenSSL incorrectly performed the x86_64
Montgomery squaring procedure. While unlikely, a remote attacker could
possibly use this issue to recover private keys. (CVE-2019-1551)

Bernd Edlinger discovered that OpenSSL incorrectly handled certain
decryption functions. In certain scenarios, a remote attacker could
possibly use this issue to perform a padding oracle attack and decrypt
traffic. (CVE-2019-1563)

References:
  https://usn.ubuntu.com/4376-1
  CVE-2019-1547, CVE-2019-1549, CVE-2019-1551, CVE-2019-1563